跳转到主要内容

在 RHEL 兼容 Linux 上部署 Silo

本页介绍如何在 RHEL 及其二进制兼容 Linux 发行版上部署 Silo。

Silo 为 x86-64 与 ARM64 发布 RPM 软件包和独立 Linux 归档。项目没有单独发布 RHEL 支持生命周期矩阵,因此已删除继承文档中的时间点版本清单。请选择仍处于发行商支持期内的版本,保持内核与系统库更新,并在生产使用前验证精确的存储与工作负载配置。

本步骤重点介绍生产级 多机多盘 (MNMD)“Distributed”配置。 MNMD 部署可提供企业级性能、可用性和可扩展性,是所有生产工作负载的推荐拓扑。

本步骤也包含对 单机多盘 (SNMD) 和 单机单盘 (SNSD) 拓扑的指导,适用于早期开发和评估环境。

注意事项

检查清单

在执行本步骤前,请先阅读我们发布的硬件、软件和安全检查清单。

纠删码校验

MinIO 会根据拓扑中的节点和驱动器总数,自动为集群确定默认的 纠删码 配置。 你可以在设置集群时配置按对象生效的 parity,也可以让 MinIO 选择默认值(生产级集群默认为 EC:4)。

校验值决定了对象可用性与磁盘存储占用之间的关系。 可使用 MinIO 纠删码计算器 选择适合你集群的纠删码校验级别。

虽然你可以随时更改纠删码校验设置,但以既有校验值写入的对象 不会 自动更新为新的校验设置。

基于容量的规划

MinIO 建议在存储使用率达到 70% 之前,预先规划足以存放 至少 2 年数据的存储容量。 过于频繁地执行 服务器池 扩容,或按“just-in-time”方式扩容,通常说明架构或规划存在问题。

例如,假设某套应用每年预计至少生成 100 TiB 数据,并以 3 年后再扩容为目标。 若在部署初期就提供约 500 TiB 可用存储,集群即可在安全满足 70% 阈值的同时,为每年的数据增长预留额外缓冲。

建议使用 MinIO 纠删码计算器,围绕具体纠删码设置进行容量规划。

步骤

1. 下载 Silo RPM 包

下载与安装获取 x86-64 或 ARM64 RPM,校验发布摘要后安装:

sudo dnf install ./silo-*.rpm

当前 Silo 发布不提供继承文档中提到的 ppc64les390x 软件包变体。

2. 查看 systemd 服务文件

.rpm 软件包会将以下 systemd 服务文件安装到 /usr/lib/systemd/system/silo.service

[Unit]
Description=Silo Object Storage Server
Documentation=https://silo.pgsty.com/docs/
Wants=network-online.target
After=network-online.target minio.service
Conflicts=minio.service
AssertFileIsExecutable=/usr/bin/silo

[Service]
Type=notify

User=silo
Group=silo
ProtectProc=invisible

EnvironmentFile=-/etc/default/minio
EnvironmentFile=-/etc/default/silo
ExecStart=/usr/bin/silo server $MINIO_OPTS $MINIO_VOLUMES

# Let systemd restart this service always
Restart=always

# Specifies the maximum file descriptor number that can be opened by this process
LimitNOFILE=1048576

# Turn-off memory accounting by systemd, which is buggy.
MemoryAccounting=no

# Specifies the maximum number of threads this process can create
TasksMax=infinity

# Disable timeout logic and wait until process is stopped
TimeoutSec=infinity

# Disable killing of Silo by the kernel's OOM killer
OOMScoreAdjust=-1000

SendSIGKILL=no

[Install]
WantedBy=multi-user.target

3. 核对服务账户与目录权限

软件包安装脚本创建 silo:silo,但不会启动或启用服务。新部署应让该账户可访问计划使用的数据目录和证书目录。

从 MinIO 迁移时,保留现有数据所有者;按软件包迁移说明silo.service 设置现有用户/组的 drop-in,不要为了改名递归修改已有数据。下列步骤的 silo:silo 适用于新部署;迁移部署应使用选定的实际服务账户。

4. 启用 TLS 连接

为 MinIO 创建或提供 传输层安全 (TLS) 证书,以自动启用 server 与客户端之间的 HTTPS 安全连接。

请将证书放置在 silo 用户/组可访问的目录中:

sudo install -d -o silo -g silo -m 0750 /opt/minio/certs
sudo install -o silo -g silo -m 0600 private.key /opt/minio/certs/private.key
sudo install -o silo -g silo -m 0644 public.crt /opt/minio/certs/public.crt

对于本地测试或开发环境,你可以使用 MinIO certgen 生成自签名证书。 例如,以下命令会生成一组带有 IP 和 DNS Subject Alternate Names (SANs) 的自签名证书,这些 SAN 与 MinIO 服务端 主机关联:

certgen -host "localhost,minio-*.example.net"

将生成的 public.crtprivate.key 放入 /path/to/certs 目录,以为 MinIO 部署启用 TLS。 应用程序可以将 public.crt 作为受信任的证书颁发机构,从而在不禁用证书校验的情况下连接到 MinIO 部署。

SILO 连接其他节点、复制目标等服务时,使用操作系统信任库和配置的 CAs 目录验证对端 TLS 证书。使用私有 CA 时,将其 CA 证书放入 /opt/minio/certs/CAs,并确保服务账户可读。仅启用服务端 TLS 并不会自动启用客户端证书认证。

有关为 MinIO 配置 TLS 的更具体指导,包括通过 Server Name Indication (SNI) 支持多域名,请参阅 网络加密(TLS)。 你也可以跳过此步骤,以在未启用 TLS 的情况下部署。MinIO 强烈 不建议 在早期开发之外的场景中进行非 TLS 部署。

5. 创建 MinIO 环境文件

/etc/default/silo 创建环境文件。 MinIO 服务将该文件作为 MinIO 以及 silo.service 文件所用全部 环境变量 的来源。

请根据你的部署拓扑修改示例。

在生产环境中使用 多机多盘(“Distributed”)部署拓扑。

# Set the hosts and volumes MinIO uses at startup
# The command uses MinIO expansion notation {x...y} to denote a
# sequential series.
#
# The following example covers four MinIO hosts
# with 4 drives each at the specified hostname and drive locations.
#
# The command includes the port that each MinIO server listens on
# (default 9000).
# If you run without TLS, change https -> http

MINIO_VOLUMES="https://minio{1...4}.example.net:9000/mnt/disk{1...4}/minio"

# Set all MinIO server command-line options
#
# The following explicitly sets the MinIO Console listen address to
# port 9001 on all network interfaces.
# The default behavior is dynamic port selection.

MINIO_OPTS="--console-address :9001 --certs-dir /opt/minio/certs"

# Set the root username.
# This user has unrestricted permissions to perform S3 and
# administrative API operations on any resource in the deployment.
#
# Defer to your organizations requirements for superadmin user name.

MINIO_ROOT_USER=minioadmin

# Set the root password
#
# Use a long, random, unique string that meets your organizations
# requirements for passwords.

MINIO_ROOT_PASSWORD=minio-secret-key-CHANGE-ME
在开发和评估环境中使用 单机多盘 部署。 对于能够容忍节点停机带来数据丢失或不可用的小型存储工作负载,也可以使用该拓扑。

# Set the volumes MinIO uses at startup
# The command uses MinIO expansion notation {x...y} to denote a
# sequential series.
#
# The following specifies a single host with 4 drives at the specified location
#
# The command includes the port that the MinIO server listens on
# (default 9000).
# If you run without TLS, change https -> http

MINIO_VOLUMES="https://minio1.example.net:9000/mnt/drive{1...4}/minio"

# Set all MinIO server command-line options
#
# The following explicitly sets the MinIO Console listen address to
# port 9001 on all network interfaces.
# The default behavior is dynamic port selection.

MINIO_OPTS="--console-address :9001 --certs-dir /opt/minio/certs"

# Set the root username.
# This user has unrestricted permissions to perform S3 and
# administrative API operations on any resource in the deployment.
#
# Defer to your organizations requirements for superadmin user name.

MINIO_ROOT_USER=minioadmin

# Set the root password
#
# Use a long, random, unique string that meets your organizations
# requirements for passwords.

MINIO_ROOT_PASSWORD=minio-secret-key-CHANGE-ME

在早期开发和评估环境中使用 单机单盘(“Standalone”)部署。 MinIO 不建议在生产环境中使用 单机部署,因为节点或其存储介质丢失会导致数据丢失。

警告

重要

SNSD 部署不支持通过添加新的 服务器池 来扩展存储。

# Set the volume MinIO uses at startup
#
# The following specifies the drive or folder path

MINIO_VOLUMES="/mnt/drive1/minio"

# Set all MinIO server command-line options
#
# The following explicitly sets the MinIO Console listen address to
# port 9001 on all network interfaces.
# The default behavior is dynamic port selection.

MINIO_OPTS="--console-address :9001 --certs-dir /opt/minio/certs"

# Set the root username.
# This user has unrestricted permissions to perform S3 and
# administrative API operations on any resource in the deployment.
#
# Defer to your organizations requirements for superadmin user name.

MINIO_ROOT_USER=minioadmin

# Set the root password
#
# Use a long, random, unique string that meets your organizations
# requirements for passwords.

MINIO_ROOT_PASSWORD=minio-secret-key-CHANGE-ME

请根据部署需要,指定其他 环境变量 或 server 命令行选项。

对于分布式部署,所有节点的 /etc/default/silo 环境文件 必须 完全一致。 可在每个节点上使用 shasum -a 256 /etc/default/silo 等工具验证其是否完全匹配。

6. 启动 MinIO 部署

使用 systemctl start silo 启动部署中的每个节点。

你可以在每个节点上使用 journalctl -u silo 跟踪启动状态。

启动成功后,MinIO 进程会输出一段部署摘要,类似如下:

Silo 对象存储服务端
Copyright: 2015-2025 MinIO, Inc.
Modifications: Copyright 2025-2026 PGSTY
License: GNU AGPLv3 - https://www.gnu.org/licenses/agpl-3.0.html
Version: RELEASE.2026-09-16T00-00-00Z (go1.27.1 linux/amd64)

API: https://minio-1.example.net:9000 https://203.0.113.10:9000 https://127.0.0.1:9000
   RootUser: minioadmin
   RootPass: minioadmin

WebUI: https://minio-1.example.net:9001 https://203.0.113.10:9001 https://127.0.0.1:9001
   RootUser: minioadmin
   RootPass: minioadmin

CLI: https://silo.pgsty.com/zh/reference/minio-mc/#quickstart
   $ mc alias set 'myminio' 'https://minio-1.example.net:9000' 'minioadmin' 'minioadmin'

Docs: https://silo.pgsty.com/zh/docs/
Status:         16 Online, 0 Offline.

在集群启动和同步期间,你可能会看到日志明显增多。

启动失败的常见原因包括:

  • MinIO 进程对指定驱动器没有读、写、列出权限
  • 驱动器不是空的,或其中包含非 MinIO 数据
  • 驱动器未正确格式化或挂载
  • 一个或多个主机无法通过网络访问

遵循我们的检查清单通常可以降低遇到这些或类似问题的风险。

7. 连接到部署

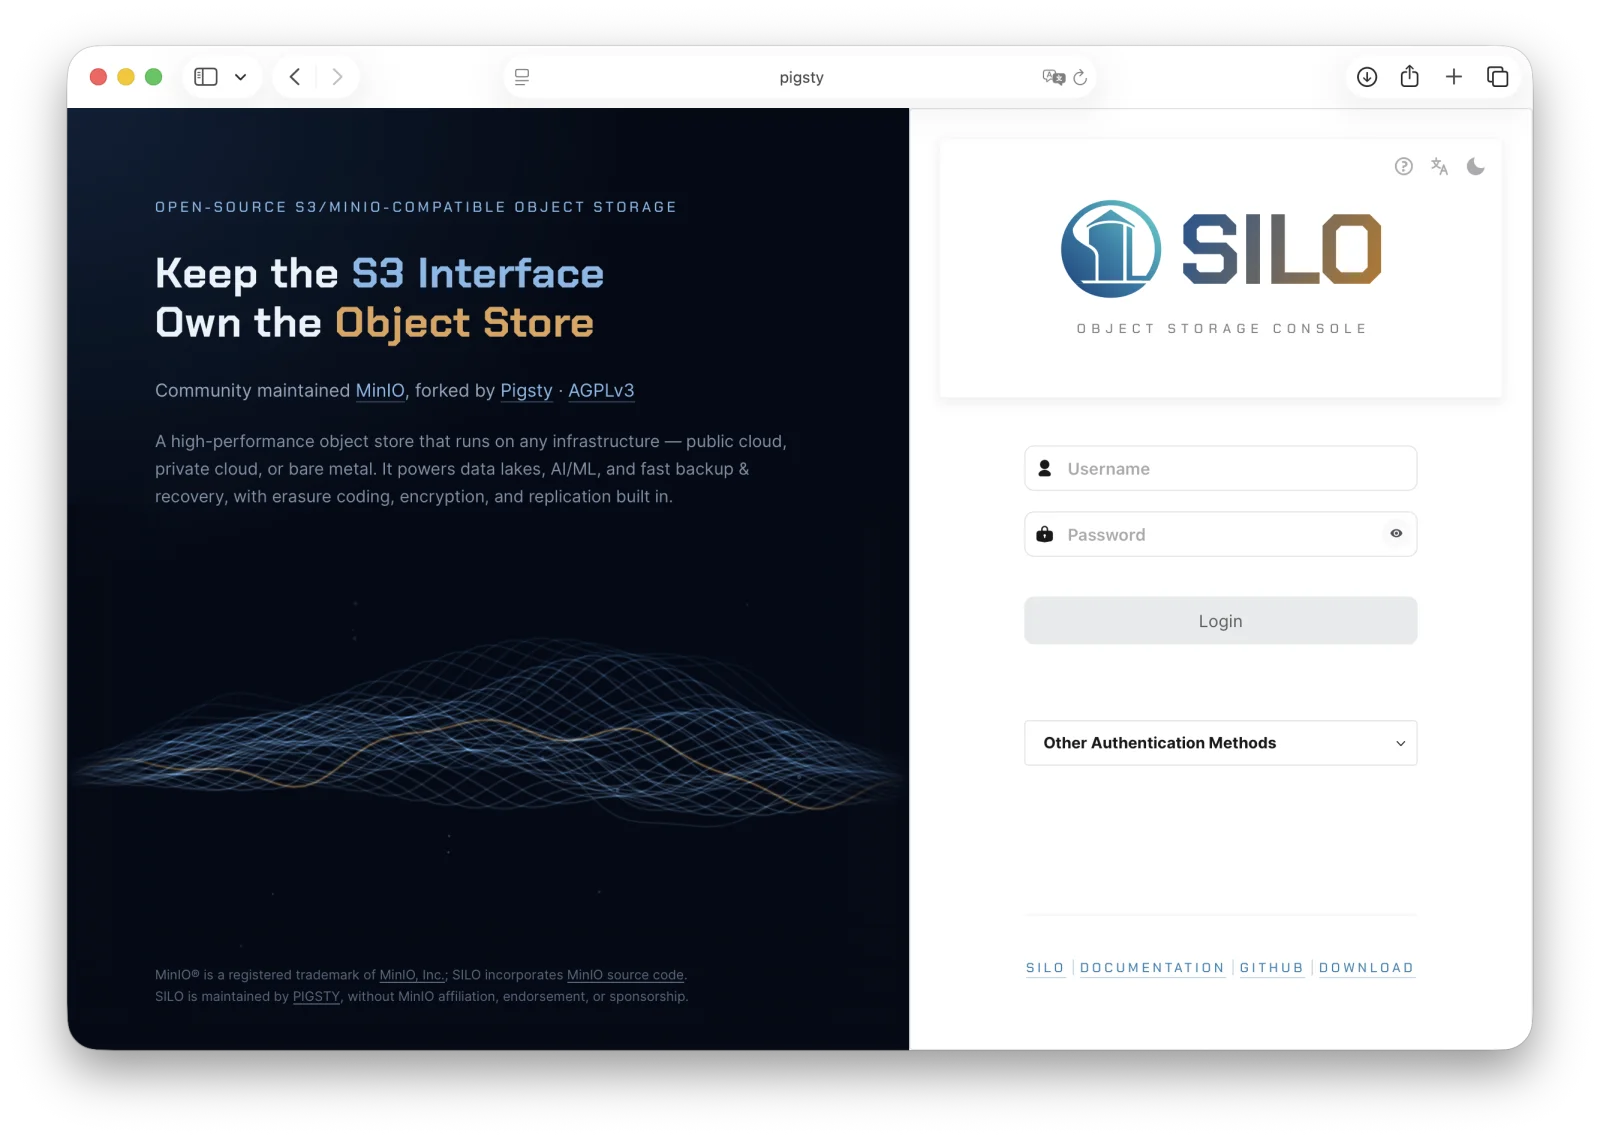
打开浏览器,并通过任一 MinIO 主机名的 :9001 端口访问 MinIO Console 登录页。 例如:https://minio1.example.com:9001

使用上一步中的 MINIO_ROOT_USERMINIO_ROOT_PASSWORD 登录。

MinIO Console 登录页

你可以使用 MinIO Console 执行常规管理任务,例如身份与访问管理、指标和日志监控,或 Server 配置。 每个 MinIO server 都包含自身内嵌的 MinIO Console。

请按照本地主机上的 mcli 安装说明 完成安装。 运行 mcli --version 验证安装结果。下文引用的 mc 命令可替换为发行包安装的 mcli,参数保持不变。

如果你的 MinIO 部署使用第三方或自签名 TLS 证书,请将 CA 文件复制到 ~/.mc/certs/CAs,以便 mc 信任该证书链。

安装完成后,为该 MinIO 部署创建一个别名:

mc alias set myminio https://minio-1.example.net:9000 USERNAME PASSWORD

请根据你的部署修改主机名、用户名和密码。 主机名可以是部署中的任意一个 MinIO 节点。 你也可以指定负责处理部署连接的负载均衡器、反向代理或类似网络控制平面的主机名。

8. 后续步骤